

Cyber Security Engineer | Senior Cybersecurity Consultant | Tech Lead
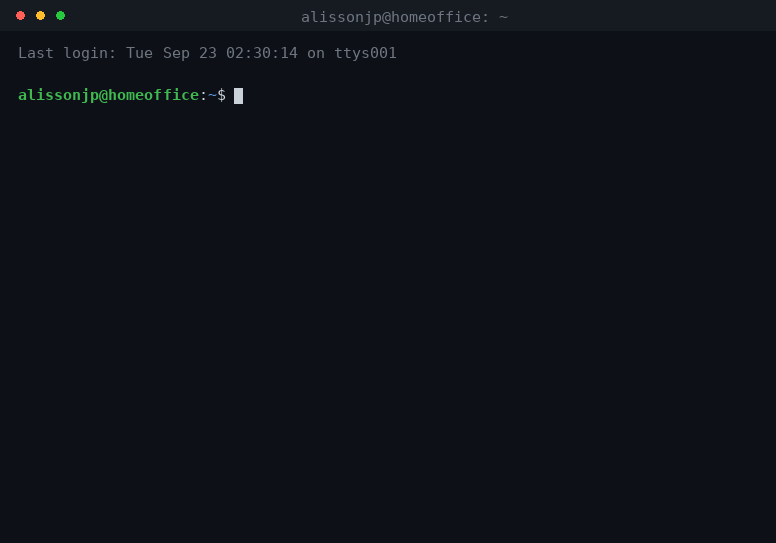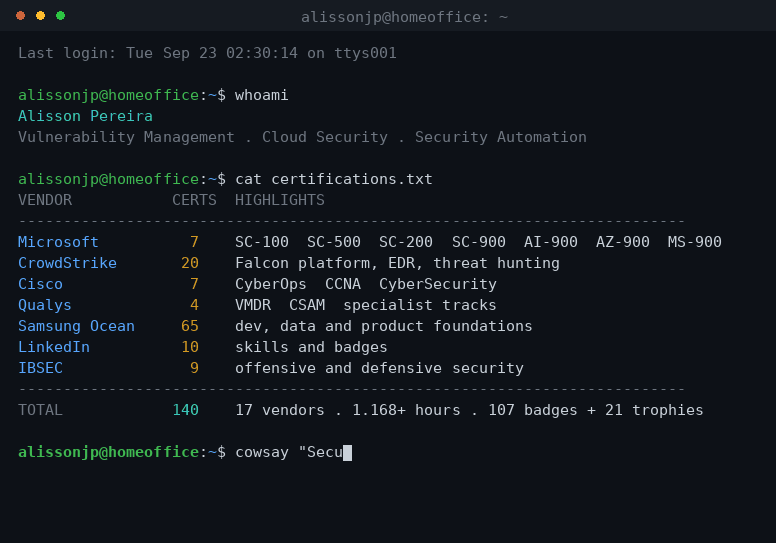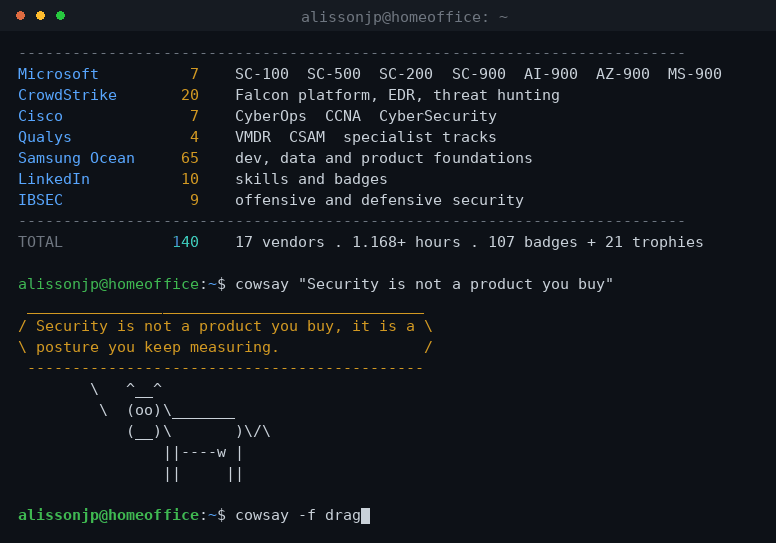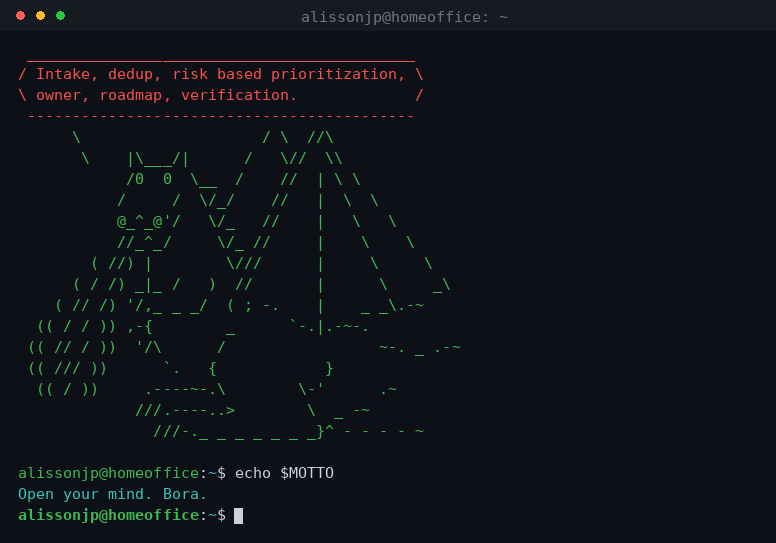
Vulnerability Management · Cloud Security · Security Automation


Vulnerability Management and Cloud Security leader with 15+ years of professional experience, delivering for large enterprises across North America, EMEA and LATAM in English speaking, multicultural teams.
What I do
- Run vulnerability management as a full cycle, not a scan report: intake, deduplication, risk based prioritization, owner assignment, remediation roadmap and verification
- Assess cloud security posture at enterprise scale and turn findings into a plan, with severity, effort, affected resources and an owner for every item
- Lead and mentor consultants and architects, raising delivery quality and shortening ramp up time for new team members
- Build the automation behind all of it, which is how high assessment volume gets delivered consistently instead of one report at a time
How I work
I turn scan output into decisions someone can own. The pipelines I build ingest cloud posture and benchmark exports, then produce a prioritized remediation roadmap, an executive readout, dashboards and a client ready package, with every recommendation traced back to its evidence.
I also build the tooling behind the delivery. Internal automation agents I designed cut assessment delivery time by roughly 80% and reduced onboarding time for new team members by about 25%, which made the practice measurably more scalable and consistent.
My early career includes national level leadership in a regulated, audit driven environment, which still shapes how I report and document.
Based in Brazil. I work in Portuguese and English.
| Domain | Tools and practices |
|---|---|
| 🤖 AI Agents & Skills | Agent and skill design, orchestration, prompt engineering, typed and auditable decisions, Microsoft Copilot |
| ☁️ Cloud Security & CSPM | Microsoft Defender for Cloud, Secure Score, Microsoft Cloud Security Benchmark, Azure Policy |
| 🛡️ Threat Detection & Response | Microsoft Sentinel, Defender XDR, KQL, MITRE ATT&CK |
| 🔍 Vulnerability Management | Qualys VMDR and CSAM, Tenable Nessus, Defender Vulnerability Management |
| 🦅 Endpoint & EDR | CrowdStrike Falcon, Microsoft Defender for Endpoint |
| 🔐 Identity & Data | Microsoft Entra ID, Conditional Access, Microsoft Purview |
| 📋 Governance & Compliance | CIS Controls, NIST SP 800-53, ISO 27001, PCI DSS, LGPD |
| ⚙️ Automation & Reporting | Python, PowerShell, KQL, Power BI, Git, GitHub Actions |


- 🚀 ~80% faster security assessment delivery, through automation agents I designed and built
- 📉 ~25% shorter onboarding for new consultants, from standardized runbooks and documentation
- 🌎 Delivering to large enterprise customers across North America, remote from Brazil
- 🎓 Mentoring and enabling other consultants on assessment quality and delivery
- 🗂️ 108 badges and 21 trophies on Microsoft Learn, plus 77+ hours of tracked learning
Five of these are public previews: the design, the decisions and sample deliverables built with fictional data. The complete implementations live in private repositories. YSAT and YSAT-JEV are published in full, under MIT.
End to end vulnerability program built with open source tooling. No finding trusts a single tool: confidence is computed from how many independent scanners agree. Preview with design rationale and sample deliverables.
|
Typed decision variant: triage composed in code from 11 atomic questions with calibrated confidence, plus a benchmark that states what it did not prove.
|
Indicator lifecycle with TTL and decay per type, unwanted software handled as versioned policy, and automatic retroactive hunting across a 30 day window.
| Typed decision variant: indicator triage decided in code from closed typed questions with calibrated confidence, with a block layer veto and blind hunt tagging.
|
Turns reference guides into a baseline of its own: plain language names, severity decided by an explicit rule, validated remediation, and a read only checker that can answer that it could not check.
|
|
🤖 YSATAn AI agent skill that disagrees with you, on purpose, with evidence. Risk first, pre mortem always, verdict changes only on new evidence.
|
⚖️ YSAT-JEVTyped judgment variant: the verdict is composed in code from atomic typed questions, with an auditable trail and a state hash.
|
Interactive single page portfolio: 140 certifications, instant search, filters by vendor and area, dark mode and shareable filtered links.
|
Source repository behind the portfolio, with every certificate, badge and course syllabus under version control. |


Open your mind!
Security is not a product you buy, it is a posture you keep measuring. Bora.